İsmail Can Akdeniz and Melis Meriç Gürel, Dokuz Eylül University. Date: 23rd of November, 2026, Monday, Time: 13:00. Place: Dokuz Eylül Univ., Tınaztepe Campus, Faculty of Science, Department of Mathematics, Classroom B254.
Abstract:
We will introduce interactive theorem proving and functional programming through Lean 4, alongside automated proof search with Aristotle and AI tools.
The foundation of computer-assisted proof verification relies on the Curry–Howard Correspondence, which establishes a direct isomorphism between logic and type theory:
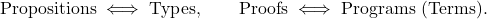
Formal Verification Principle. Let  be a mathematical proposition formalized as a type in Lean~4. A term
 is accepted by Lean’s kernel if and only if
 constitutes a logically complete and error-free proof of .
We will demonstrate how classical analytical statements are translated into formal Lean syntax using the \textbf{Mathlib} library. Specifically, we will examine the convergence of real sequences; let  be a sequence of real numbers converging to zero and
 be a bounded sequence of real numbers. We will formalize and prove that the product sequence
 also converges to zero:
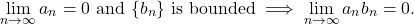
We will reinforce this proof with live demonstrations in Lean’s Tactic Mode and illustrate how AI-assisted provers like Aristotle help bridge incomplete proof steps (sorry). If time permits, we shall discuss other examples.
This seminar, as part of our graduation project titled Proofs, Machine-Checked: The Power of Lean 4, serves as an accessible introduction to formalizing undergraduate mathematics and verifying proofs with absolute logical certainty.